A Set-Cookie header is a one-line contract with the browser, and most of it is silent. Nothing tells you when an attribute was rejected, when a lifetime was truncated, or when the cookie was never stored at all. This page walks through what each attribute does, which combinations browsers refuse, and how to read the report above.
What a Set-Cookie header holds
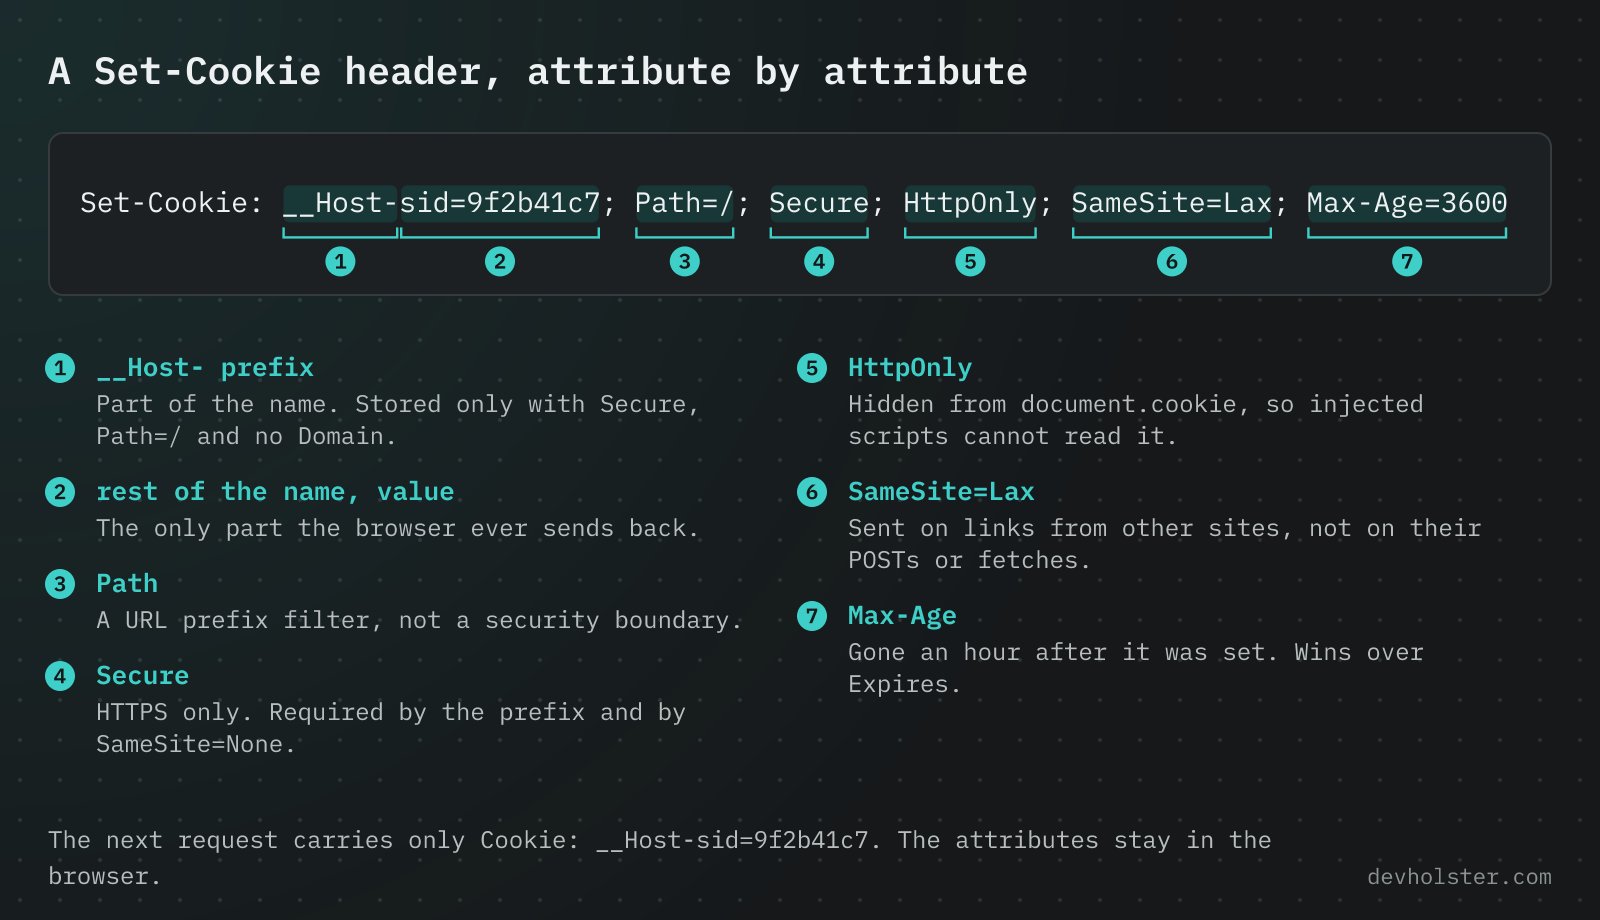
The structure is simple: a name, a value, then a list of attributes separated by semicolons.
| Part | Example |
|---|---|
| name and value | sessionid=9f2b41c7 |
| attributes | Path=/; Secure; HttpOnly; SameSite=Lax; Max-Age=3600 |
Only the name and the value ever come back. The browser stores the attributes, uses them to decide when to send the cookie, and then sends a Cookie header containing nothing but name=value pairs. Your server cannot see the Path, the expiry or the SameSite setting of an incoming cookie, which is why a cookie that arrives with an unexpected value usually means two cookies of the same name exist on different paths.
How to read the report
Paste one Set-Cookie line per row. A leading Set-Cookie: is optional, an HTTP status line is ignored, and a Cookie: request header is recognised and analysed differently.
- Attributes. Every attribute present, plus three computed rows: the real lifetime in days rather than seconds, the byte size, and a plain sentence saying which hosts and paths the cookie will be sent to.
- Findings. Errors first. An error means a browser rejects or truncates something. A warning means it works but is worth changing. Information is context, not a problem.
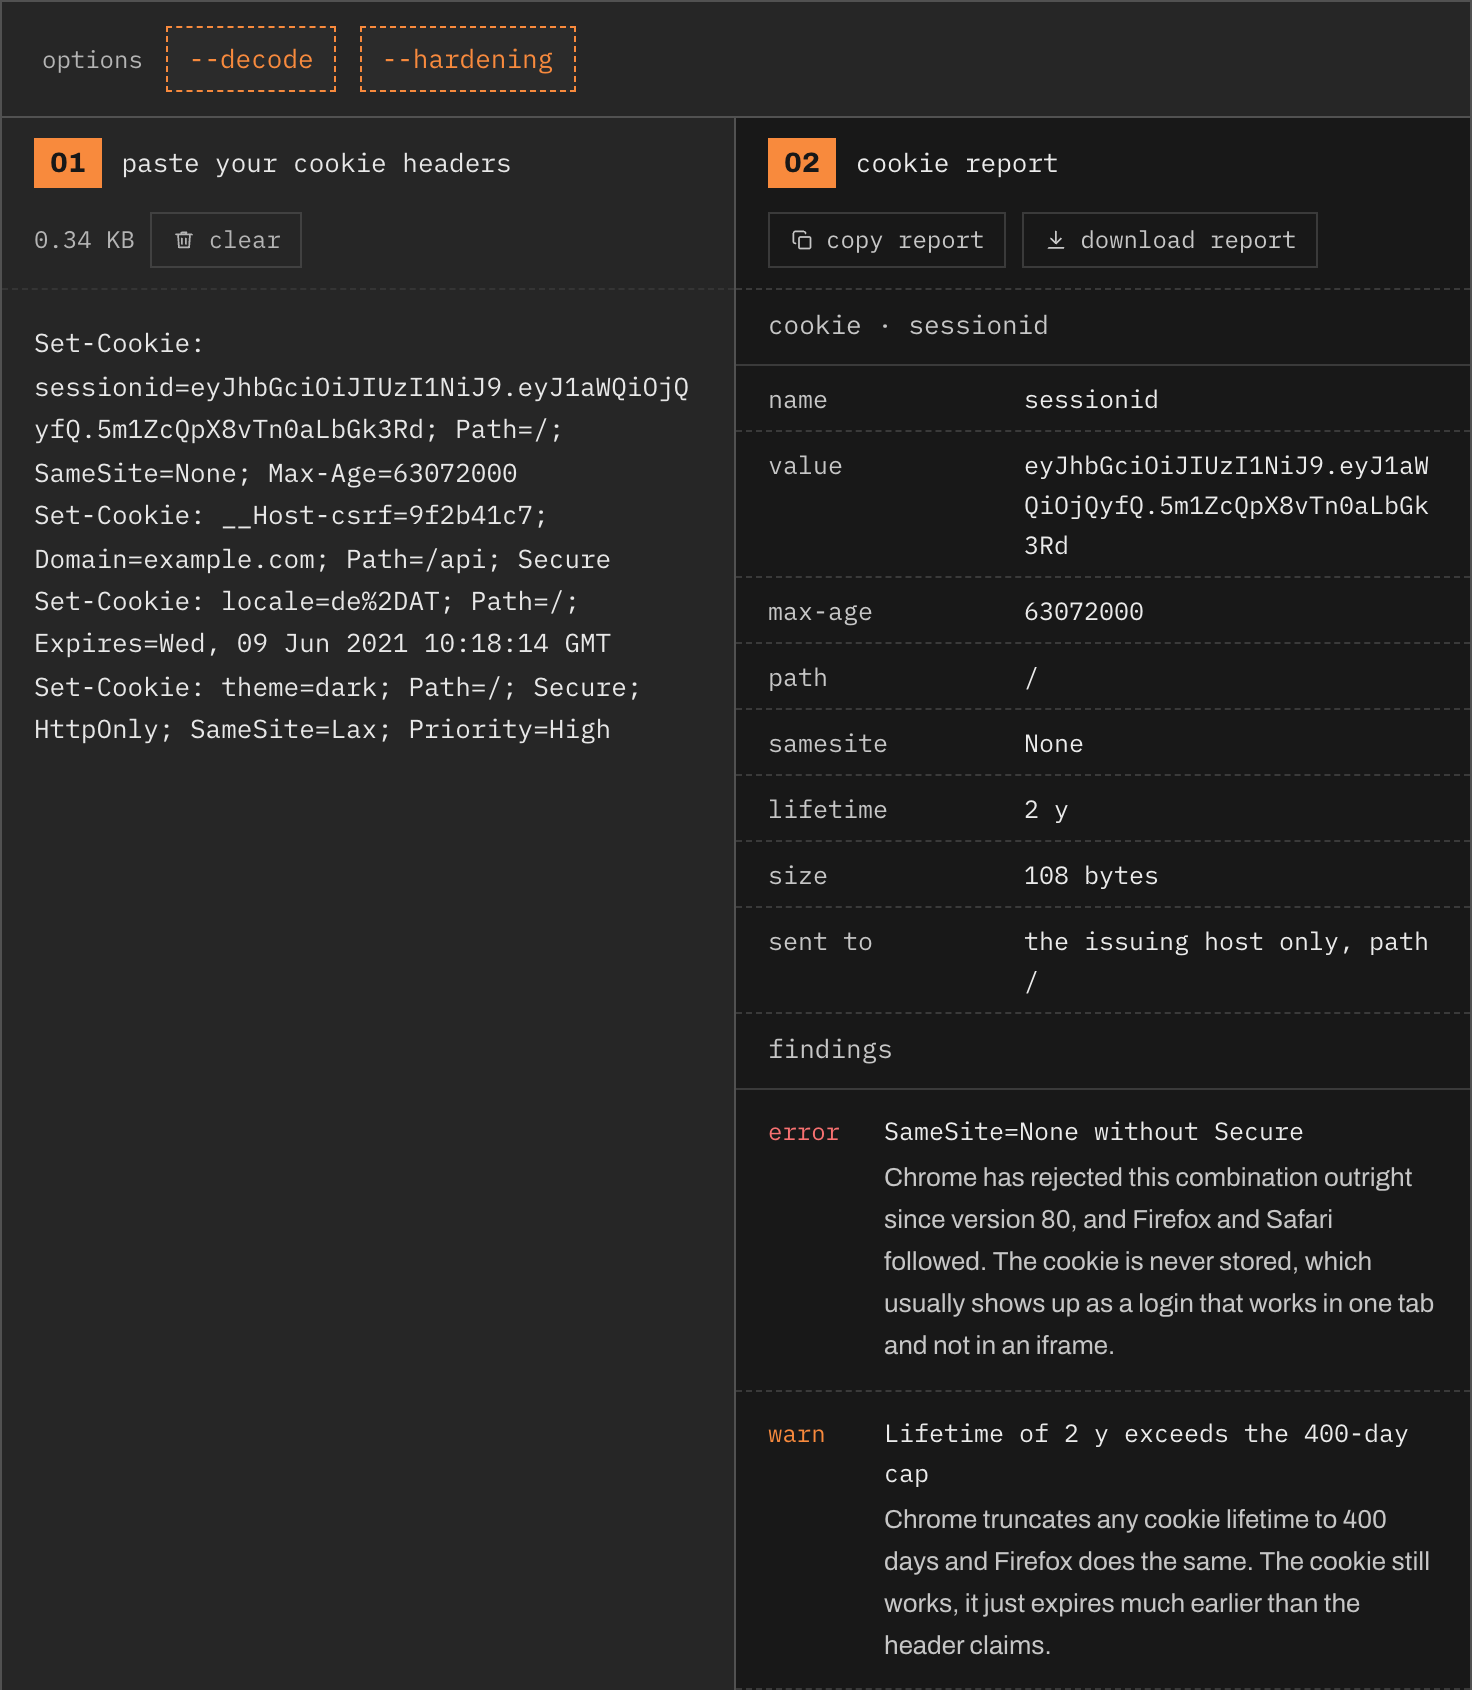
SameSite=None without Secure, so browsers refuse to store it, and its two-year Max-Age would be cut to 400 days anyway. The computed rows read 2 y, 108 bytes and the issuing host only. Below the cut the report continues with more findings for this cookie and a block for each of the other three.--decode
Percent-decodes the value, so de%2DAT reads as de-AT and a JSON payload becomes legible. Most frameworks encode cookie values on the way out, which is why raw headers are full of %22 and %3A.
--hardening
Adds the advisory checks on top of the hard rules: a missing HttpOnly, a Domain attribute that widens the cookie to every subdomain, and values shaped like a JWT. Turn it off when you are debugging a specific rejection and want only the reasons the browser itself cares about.
Every attribute, explained
| Attribute | Effect | Notes |
|---|---|---|
Expires | Absolute expiry date | Must be an IMF-fixdate, Wed, 21 Oct 2026 07:28:00 GMT. Unparseable values are ignored, turning the cookie into a session cookie. |
Max-Age | Lifetime in seconds | Wins over Expires wherever both are present. Max-Age=0 deletes the cookie. |
Domain | Widens the cookie to subdomains | Absent means the exact host only, which is the safer default. The leading dot is ignored. |
Path | Restricts by URL prefix | Defaults to the directory of the request, not to /. It is not a security boundary; scripts on the same origin reach every path. |
Secure | HTTPS only | Required by SameSite=None, by Partitioned, and by both name prefixes. |
HttpOnly | Hidden from JavaScript | The single most effective thing you can do about session theft through XSS. |
SameSite | Cross-site behaviour | Strict, Lax or None. Missing means Lax in current browsers. |
Partitioned | CHIPS, one jar per top-level site | Requires Secure. For embedded content that needs its own state per host. |
Priority | Eviction order under pressure | Chrome only, Low, Medium or High. Other browsers ignore it. |
Anything else is not an attribute. Browsers drop unknown attributes without a word, so a mistyped HttpsOnly or Same-Site looks exactly like a correct header until you notice the cookie behaving as if the attribute were absent. The report flags them for that reason.
SameSite in practice
SameSite decides whether the cookie rides along when another site triggers a request to yours. The three values differ in one dimension, how much cross-site traffic still carries the cookie.
| Request | Strict | Lax | None |
|---|---|---|---|
| Same site | sent | sent | sent |
| Link from another site | not sent | sent | sent |
| Cross-site form POST | not sent | not sent | sent |
| Iframe, image, fetch | not sent | not sent | sent |
Two details cause most of the confusion. The first is that Strict breaks the arriving-from-elsewhere case: a user who clicks a link in an email to a page behind a login lands logged out, because the cookie was not sent on that navigation. The usual pattern is a Lax session cookie plus a Strict cookie for the operations that matter.
The second is that "same site" is not "same origin". It compares registrable domains, so app.example.com and api.example.com are the same site and a request between them is not cross-site, despite being cross-origin and therefore subject to CORS. Mixing the two concepts up is how people end up adding SameSite=None to a cookie that never needed it.
Chrome keeps one compatibility exception, sometimes called Lax-allowing-unsafe: a cookie younger than two minutes is still sent on a top-level cross-site POST. It exists to keep older single-sign-on flows working and it is not something to design around.
Why a cookie is silently dropped
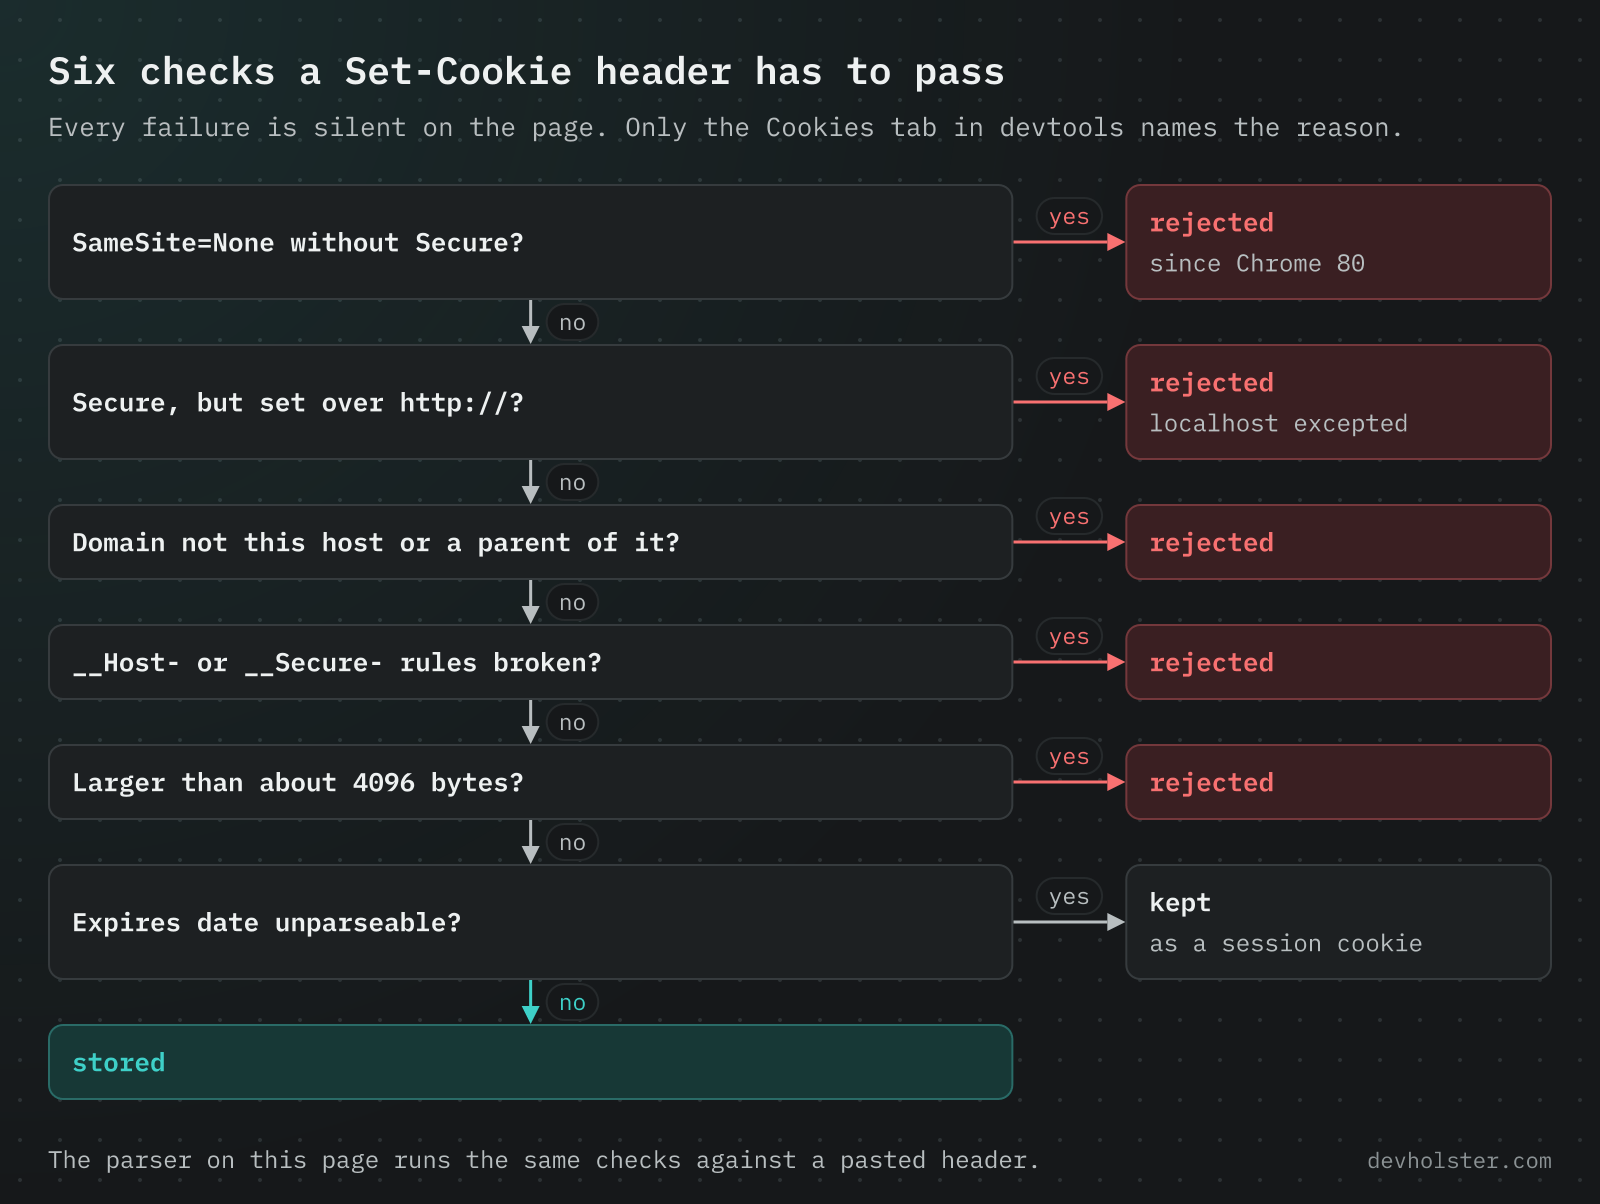
Rejection is the frustrating part of cookies, because the response looks fine and nothing appears in the browser. These are the reasons, roughly in the order they show up in real bug reports:
- SameSite=None without Secure. Rejected since Chrome 80 in February 2020. Typically appears as an integration that works in your own tab and not inside a customer's iframe.
- Secure over plain HTTP. A local development server on
http://cannot set a Secure cookie.http://localhostis treated as a secure context, other hostnames pointed at 127.0.0.1 are not. - A Domain that does not match. A host can set a cookie for itself or for a parent domain, but not for an unrelated one and not for an entry on the Public Suffix List.
- Broken prefix rules.
__Host-with a Domain attribute, or__Secure-without Secure. - Size. Above roughly 4096 bytes for name, value and attributes together, the cookie is discarded.
- An invalid Expires date. Not a rejection exactly, the attribute is just ignored, and the persistent cookie you wanted becomes a session cookie.
Chrome devtools shows all of these: open the Network panel, select the response, and the Cookies tab lists rejected cookies with a strike-through and a tooltip naming the reason. The tool above answers the same question from the header alone, which is what you have when the header came from a log, a curl run or a colleague.
The __Host- and __Secure- prefixes
Both prefixes are enforced by name. The browser sees the prefix and refuses to store the cookie unless the rules hold.
| Prefix | Requires | What it buys |
|---|---|---|
__Secure- | Secure, set over HTTPS | The cookie cannot have been written by a plain HTTP response. |
__Host- | Secure, Path=/, no Domain | The cookie is locked to one exact host and no subdomain can overwrite it. |
The attack __Host- closes is cookie tossing. Subdomains share a cookie jar with the parent domain, and a cookie set on blog.example.com for .example.com arrives at example.com looking exactly like one the main app set. The server cannot tell them apart, because the Cookie header carries no Domain. Anyone who controls any subdomain, including a forgotten staging box or a hosted marketing tool, can therefore write cookies your application trusts. Renaming a CSRF token to __Host-csrf costs one line and removes the whole class.
Size and lifetime limits
Cookies are small, and every one of them is sent with every request to the domain, including images and API calls. The numbers worth knowing:
- About 4096 bytes per cookie, counting name, value and attributes. Over that, browsers drop it.
- Around 180 cookies per domain in Chrome, with a global cap in the low thousands. Once it fills, cookies are evicted, and Priority decides the order.
- 400 days maximum lifetime since Chrome 104 in August 2022, matched by Firefox. Longer values are accepted and truncated.
- Seven days in Safari for cookies written by JavaScript through document.cookie, under Intelligent Tracking Prevention. Cookies set by a Set-Cookie header are not affected.
- 8 KB per request header line on nginx by default, 8190 bytes on Apache. Cross it and you get a 400 before your application ever runs.
Keep an identifier in the cookie and the state on the server. A session cookie that carries a serialised user object works fine in development, then someone adds a permissions array and every request to the domain grows by two kilobytes. The guide on SameSite, Secure and HttpOnly covers the attribute history in more depth, and if you are deciding where to keep a token in the first place, localStorage vs cookies is the relevant one.
Decoding a cookie value
A cookie value is often several encodings stacked on top of each other. Read it from the outside in, and stop at the layer that is a signature or a ciphertext, because nothing on the client can open those.
| The value looks like | What it is | How to read it |
|---|---|---|
%7B%22id%22%3A42%7D | percent-encoded, here a JSON object | --decode above, or decodeURIComponent. Frameworks encode on the way out because ;, ,, spaces and quotes are illegal in a cookie value. |
eyJhbGciOiJIUzI1NiJ9.eyJ1aWQiOjQyfQ.5m1Z… | a JWT, three Base64URL segments | The report flags it under --hardening. The JWT decoder shows header, payload and expiry. Anyone holding the cookie can read the payload. |
s%3Aabc123.hN4x… | express-session, s: plus session id plus HMAC signature | The part before the dot is the key in your session store, the part after proves nobody edited it. Nothing to decode, the data lives on the server. |
eyJ1c2VyX2lkIjo0Mn0.aBcD12.k9Xy… or .eJw… | Flask session, Base64URL JSON plus timestamp plus signature, zlib-compressed when it starts with a dot | Base64-decode the first segment to read it. Verifying the signature needs the SECRET_KEY, reading does not. |
eyJpdiI6… that decodes to "iv", "value", "mac" | Laravel encrypted cookie | Base64 wraps JSON, but the value inside is AES-encrypted with APP_KEY. This one you cannot read from the outside. |
BAh7B0kiD3Nlc3Npb25faWQ…--a1b2c3 | Rails signed cookie, Base64 then -- then HMAC. Rails 5.2 and newer encrypt by default, which adds two more -- parts | Signed ones decode to a Marshal or JSON blob. Encrypted ones need secret_key_base. |
.eJyrVk…:1tX2k:q7Zx… | Django signed-cookie session, Base64 (compressed when it starts with a dot), timestamp and signature separated by colons | Base64-decode the first part. The default Django session engine stores a plain 32-character id instead, with nothing inside. |
9f2b41c7a0d3…, 32 hex characters | an opaque session id | Nothing to decode. The value is a lookup key, and the Base64 decoder will hand you garbage for it, which is the tell. |
Decoding is also where a long Cookie header becomes legible. Paste the whole Cookie: line and the report lays it out one pair per row with the byte cost of each, which is the closest thing to a cookie formatter that makes sense for a header with no line structure of its own.
Parsing cookies in JavaScript and Node.js
Three different jobs hide behind "parse cookies in JavaScript", and they need three different tools.
document.cookie in the browser
document.cookie returns every cookie the script may see as one string, a=1; theme=dark, with no attributes. Parsing it is a few lines, and the trap is that values may be percent-encoded, so decode after splitting, and split on the first = only, because a Base64 value ends in = signs:
const cookies = Object.fromEntries(document.cookie.split('; ').filter(Boolean).map((c) => {
  const i = c.indexOf('=');
  return [c.slice(0, i), decodeURIComponent(c.slice(i + 1))];
}));
The js-cookie library wraps exactly this plus the writing side in about two kilobytes, and the newer cookieStore API returns parsed objects asynchronously where a browser ships it.
cookie-parser in Express
The npm package cookie-parser is Express middleware. It reads the incoming Cookie header into req.cookies, and when you pass it a secret it verifies signed cookies (the s: format from the table above) into req.signedCookies, with tampered ones showing up as false:
import cookieParser from 'cookie-parser';
app.use(cookieParser(process.env.COOKIE_SECRET));

app.get('/me', (req, res) => {
  req.cookies.theme;            // 'dark'
  req.signedCookies.sessionid;  // '9f2b41c7', or false if the signature failed
});
It does not parse Set-Cookie, and it only JSON-decodes values that carry the j: prefix it writes itself. Underneath sits the cookie package, the right choice when you need parse() and serialize() without Express. Fastify and Hono ship their own equivalents with the same shape.
Set-Cookie and the comma trap
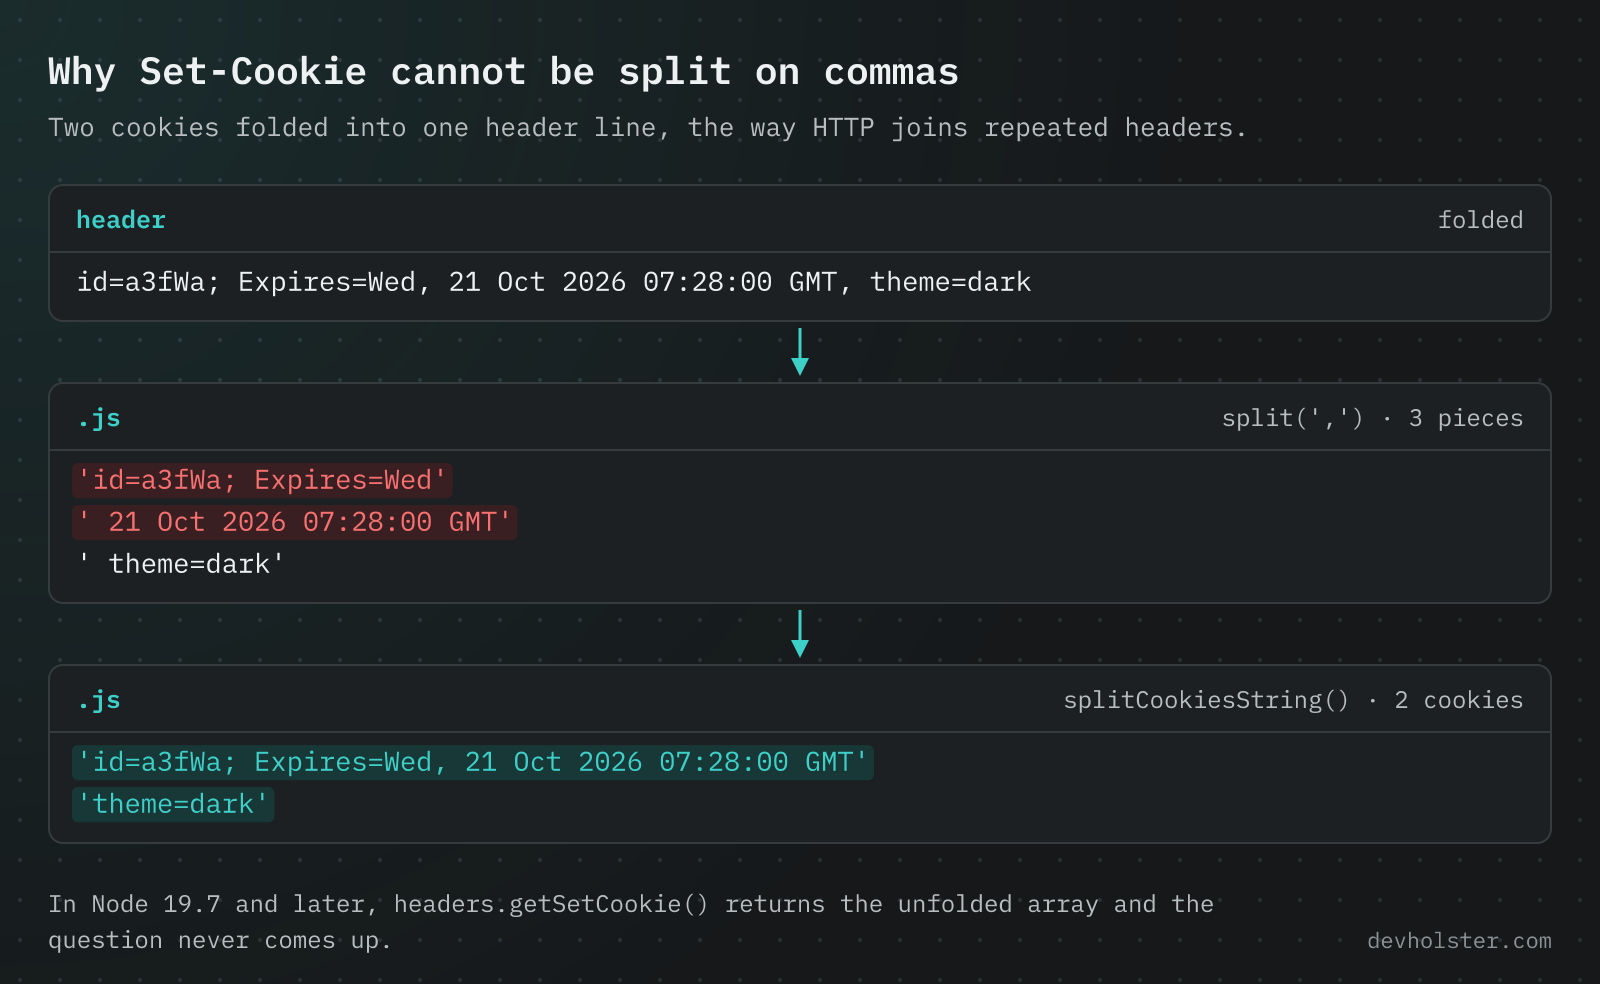
The trap is the comma. HTTP folds repeated headers into one comma-separated line, but Set-Cookie values contain commas themselves, inside every Expires date, so a naive split on the comma turns two cookies into four fragments. Browsers dodge the question by hiding the header from JavaScript entirely, Set-Cookie is a forbidden response header for fetch and XHR.
In Node you get at it in two ways. The bundled fetch has response.headers.getSetCookie(), which returns the unfolded array (added in Node 19.7 and backported to 18.15). The classic http module special-cases the header, res.headers['set-cookie'] is always an array. For everything else, proxies, tests, headers copied out of a log, the npm package set-cookie-parser does the splitting and the attribute parsing in one step:
import { parseSetCookie, splitCookiesString } from 'set-cookie-parser';

const res = await fetch('https://example.com/login', { method: 'POST' });
parseSetCookie(res);
// [{ name: 'sessionid', value: '9f2b41c7', path: '/', secure: true, httpOnly: true }]

splitCookiesString('id=a3fWa; Expires=Wed, 21 Oct 2026 07:28:00 GMT, theme=dark');
// ['id=a3fWa; Expires=Wed, 21 Oct 2026 07:28:00 GMT', 'theme=dark']
parseSetCookie accepts a fetch Response, a Node response object, an array or a single header string, and returns one object per cookie with expires as a real Date. Two defaults worth knowing: values are run through decodeURIComponent (turn it off with decodeValues: false), and since version 3 a combined header string is split automatically, so splitCookiesString is only needed when you want the raw lines back. What no parser can restore is anything the browser decided. A parsed object tells you what the server asked for, not whether the cookie was stored, and that second question is what the report above answers.
Cookie parsing questions
Is it safe to paste a session cookie into an online cookie parser?
Only into one that parses in your browser. A Set-Cookie line from a real response contains a live session token, so a server-side parser gets a working login to your application, and it will sit in an access log long after you closed the tab. The parsing here is JavaScript running in your tab: the header is never uploaded, never logged, and the page keeps working with the network disconnected. Check the Network panel in devtools while you type if you want proof that nothing leaves.
What does SameSite=Lax mean?
SameSite=Lax sends the cookie with same-site requests and with top-level navigations that use a safe method, so following a link from another site carries the cookie but an image, an iframe, a form POST or a fetch from another origin does not. It has been the default in Chrome since version 80 and in Firefox since 2020, which means a cookie with no SameSite attribute behaves as Lax. Strict drops even the link case, and None sends the cookie everywhere but requires the Secure attribute.
Why is my cookie not being set?
In order of how often it happens: SameSite=None without Secure, which browsers reject outright; a Domain attribute that does not match the response host; the response came over plain HTTP while the cookie asked for Secure; a __Host- or __Secure- prefix whose rules are broken; an Expires date in the past; or the cookie is larger than about 4 KB. None of these produce an error you can catch, the cookie simply never appears. Chrome devtools shows the reason under Network, then the request, then the Cookies tab, where rejected cookies are listed with a strike-through.
What is the difference between Secure and HttpOnly?
Secure controls the transport: the cookie is only sent over HTTPS, so it cannot be read by anyone watching a plain HTTP request. HttpOnly controls the reader: the cookie is hidden from document.cookie, so JavaScript on the page cannot see it and an XSS payload cannot exfiltrate it. They protect against different attackers and both belong on a session cookie. Neither prevents the cookie being sent on cross-site requests, which is what SameSite is for.
How long can a cookie last?
400 days, in practice. Chrome capped cookie lifetimes at 400 days in version 104, released in August 2022, and Firefox followed. A Max-Age of 63072000 (two years) is therefore accepted, stored, and quietly truncated to 400 days. Safari is stricter for cookies set by JavaScript: its Intelligent Tracking Prevention caps those at seven days, which is why a "remember me" that works in Chrome can expire within a week on iOS.
What is the __Host- prefix?
A cookie name starting with __Host- is a contract enforced by the browser: the cookie must have Secure, must have Path=/, and must have no Domain attribute. Break any of those and the cookie is rejected. The payoff is that a subdomain cannot overwrite it, which closes the cookie-tossing attack where a compromised or third-party subdomain writes a cookie the main domain then trusts. For CSRF tokens it is close to free security and still barely used.
What is a Partitioned cookie?
Partitioned marks a cookie as CHIPS, Cookies Having Independent Partitioned State. The cookie is stored in a jar keyed to the top-level site rather than shared across every site that embeds you, so an embedded widget can keep state per host without being a cross-site tracker. It requires Secure, and reading it from a different top-level site returns nothing. It is the supported way to keep third-party iframes working as browsers narrow unpartitioned cross-site cookies.
How do I decode a cookie value?
Percent-decode it first, then look at the shape. eyJ means Base64 JSON or a JWT, s%3A means an express-session id with a signature, and 32 hex characters mean an opaque session key with nothing inside to decode.
How do I parse cookies in Express?
npm install cookie-parser, then app.use(cookieParser()) and read req.cookies.name. Pass a secret to get verified signed cookies in req.signedCookies.
Can JavaScript read an HttpOnly cookie?
No, and that is the point. document.cookie skips them, the browser still sends them, and a frontend needing the value should ask an API.
What causes "400 Request Header Or Cookie Too Large"?
The Cookie header the browser sends grew past what the server accepts. nginx allows 8 KB per header line by default through large_client_header_buffers, and Apache 8190 bytes through LimitRequestFieldSize. Because every cookie on the domain is sent with every request, a handful of analytics and consent cookies plus a fat session gets there faster than people expect. Paste the Cookie header into this tool and it shows the byte cost of each pair, which is usually enough to identify the one to move into server-side storage.
What is the difference between the Set-Cookie and Cookie headers?
Set-Cookie is the response header and carries the attributes. Cookie is the request header and carries only name=value pairs, so the server never sees Path or expiry.
Do cookies work across subdomains?
Only if you ask for it. Without a Domain attribute a cookie is sent to the exact host that set it and nowhere else. With Domain=example.com it goes to example.com and every subdomain, including staging, the blog and anything a third party runs for you. The leading dot in ".example.com" has been meaningless since RFC 6265; both forms behave the same. A cookie cannot be widened to a parent domain that does not match the response host, so shop.example.com cannot set a cookie for example.org, and no site can set one for a public suffix such as .co.uk.
Are third-party cookies still usable?
Partly, and it depends on the browser. Safari has blocked third-party cookies by default since 2020 and Firefox partitions them through Total Cookie Protection since 2022, so in both a cross-site cookie is either absent or isolated per top-level site. Chrome reversed its plan to remove them and kept them available, while pushing CHIPS as the supported route for embedded content that needs state. Building anything new on unpartitioned third-party cookies is a bad bet; Partitioned with Secure is the version that keeps working.